Go Beyond Alerts With eSentire MDR
Cybersecurity teams face a constant stream of alerts. But receiving alerts is only part of the equation.
Effective protection requires speed, visibility, and expert response. Organizations need to know which threats matter, what is happening across their environment, and how to respond before an incident becomes a larger problem.
That’s where Managed Detection and Response (MDR) can make a difference.
Alerts Aren’t Enough
A high volume of security alerts doesn’t necessarily mean an organization is well protected.
Without the right context and expertise, important threats can be buried among false positives and routine notifications.
An effective MDR solution combines technology with security expertise to help identify real threats and take action quickly.
Detect Threats Around the Clock
Cyberattacks don’t follow a 9-to-5 schedule.
Threat actors can target organizations at any time, which means security monitoring needs to continue around the clock.
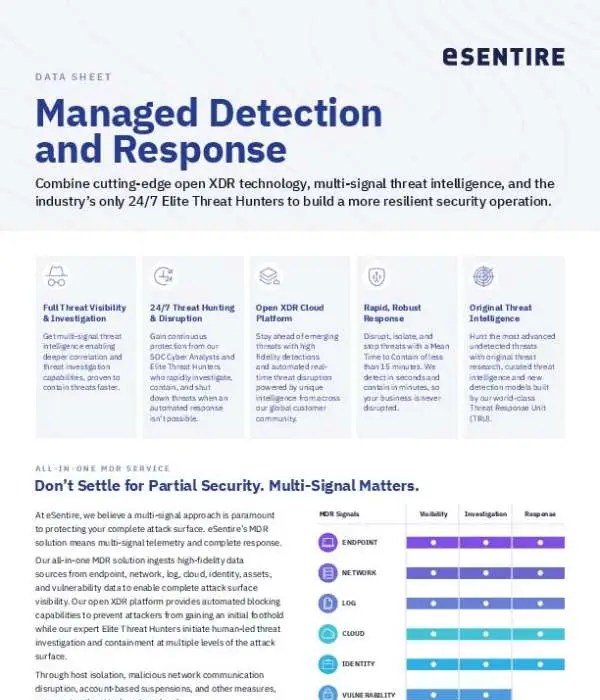
eSentire MDR provides 24/7 threat hunting, helping security professionals continuously look for suspicious activity and potential threats across an organization’s environment.
Gain Greater Visibility
You can’t protect what you can’t see.
Modern IT environments can span endpoints, cloud services, identities, applications, and other connected systems.
eSentire’s MDR approach is designed to provide greater visibility across the environment, helping security teams better understand potential risks and suspicious activity.
Respond When It Matters
Detection is only the beginning.
Once a threat is identified, organizations need to determine what happened and take appropriate action.
MDR combines monitoring, investigation, and response capabilities to help organizations move from identifying threats to addressing them.
Faster response can help limit the potential impact of an attack and reduce disruption to the business.
Connect Your Security Tools
Organizations often rely on multiple security technologies.
Managing those tools separately can create gaps in visibility and make investigations more difficult.
eSentire MDR includes open XDR integration, helping organizations connect security data and technologies to create a more coordinated approach to threat detection and response.
Global Security Expertise
Cybersecurity requires more than software.
Security teams need experienced professionals who understand how attacks work and know how to investigate suspicious activity.
eSentire’s global Security Operations Center (SOC) provides access to security expertise designed to help organizations monitor, investigate, and respond to threats.
Evaluate MDR Beyond the Feature List
When comparing MDR providers, it’s important to look beyond the number of alerts a platform can generate.
Consider questions such as:
- How quickly can threats be investigated?
- Is threat hunting available 24/7?
- How much visibility does the solution provide?
- Can it integrate with your existing security tools?
- Who responds when a serious threat is detected?
- Does the provider have the expertise to support your team?
These factors can help organizations determine whether an MDR solution provides meaningful protection rather than simply generating more alerts.
Discover the eSentire Difference
The featured datasheet explains the capabilities that set eSentire MDR apart, including 24/7 threat hunting, open XDR integration, and a global SOC.
Download the datasheet to learn what to look for when evaluating MDR solutions and discover how eSentire combines technology and human expertise to strengthen cyber defense.
Ready to take your security strategy beyond alerts? Contact Tech Hero to discuss your current environment and explore how eSentire MDR can help improve threat detection, visibility, and response.